Skip to content
Cybersecurity

Watchpost: Security uplift for a growing SaaS company

An authorised penetration test, cloud hardening and a SOC 2 readiness programme that clears the way for enterprise deals.

Sector
B2B SaaS
Typical client
Software vendor preparing for enterprise customers
Typical timeline
14 weeks
Typical team
2 security engineers
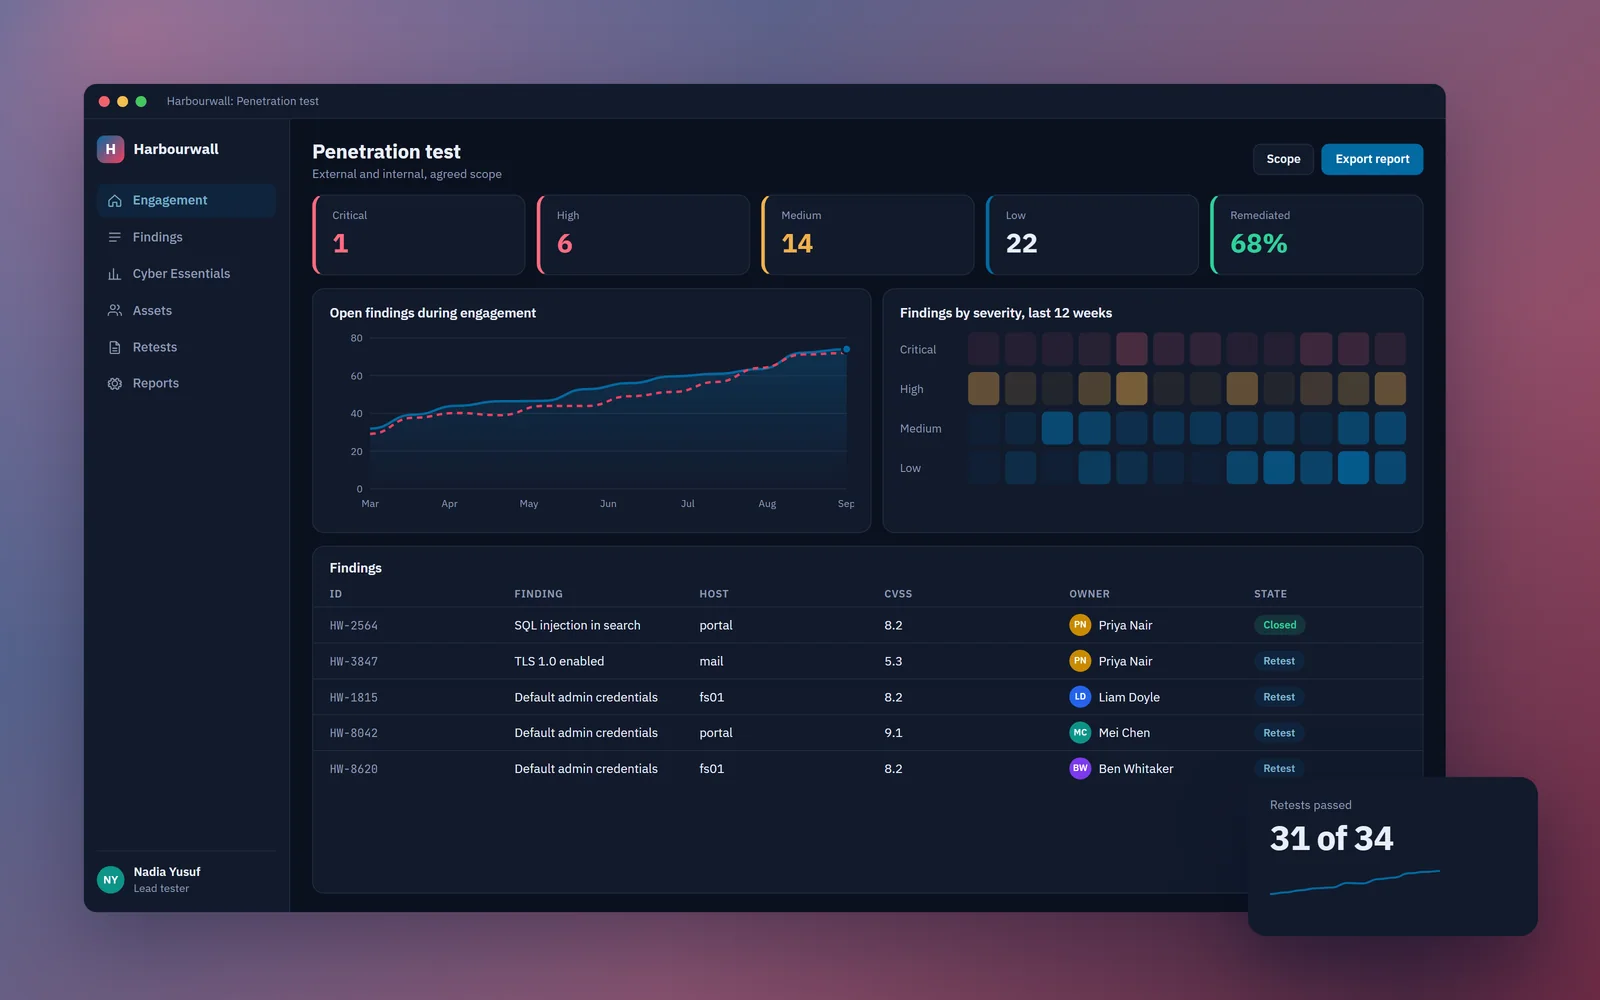
Security posture dashboard with open findings, trends and severity heatmap
Control tracker mapping evidence and ownership to SOC 2 criteria
Finding record with exploit path, remediation plan and verification history

About this project

Growing software companies reach a point where enterprise buyers start sending security questionnaires they cannot yet answer. Controls exist informally but there is little evidence.

This programme fixes the highest-risk gaps first, then builds lasting habits: least-privilege access, automated scanning and a control tracker that collects evidence as work happens.

Objectives

  • Find and close realistic attack paths before customers ask
  • Reduce cloud permissions to the least required
  • Be ready for a SOC 2 Type I audit

What’s delivered

  • Authorised web, API and cloud penetration test
  • IAM redesign and secrets management rollout
  • SAST, dependency and secret scanning in CI
  • Policies, evidence collection and incident plan
  • Retest and customer-ready attestation letter

Target outcomes

0

open critical findings

100%

findings retested

<7 days

critical fix objective

Type I

SOC 2 audit readiness

Technology

  • Burp Suite
  • Prowler
  • Semgrep
  • AWS IAM
  • Vanta

Services involved

Have a similar challenge?

Book a free consultation. We’ll scope your project, pressure-test the plan and give you an honest estimate, with no commitment required.